JSON Payload Exercise
This chapter walks step by step through obtaining an access token from Auth0 using the Client Credentials grant with a JSON payload. The flow is identical to the URL-encoded exercise. Only the Content-Type and Payload fields change.
Prerequisites
- A free Auth0 developer account. See the Before Running the OAuth Tutorial chapter.
- A QIE version that supports OAuth 2.0 on Web Service Connections.
Step 1: Gather the Auth0 application details
Log in to your Auth0 Dashboard and open the Auth0 Management API (Test Application) application that was created in your tenant by default. Copy the Domain, Client ID, and Client Secret from the Settings tab.
Step 2: Create the Web Service Connection
In QIE, navigate to the Web Service Connections page and click New.
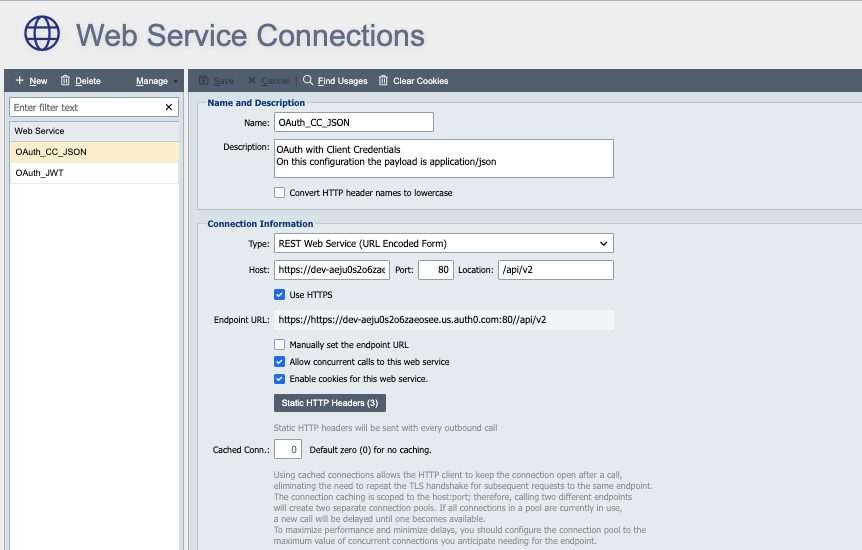
Name and Description
Enter a Name and Description for the connection. The Name is how mapping nodes and destination nodes reference the connection. Generally, the Name is associated with the Resource Server, not with the Identity Provider.
Connection Information
Configure the Type, Host, Port, Location, and any other connection details that describe how to reach the Resource Server.
SSL
Configure the trust store and (if needed) client certificate that secures the connection to the Resource Server.
Note
The Name and Description, Connection Information, and SSL fields are not the Identity Provider's settings. They describe the Resource Server you are connecting to. This could be a FHIR server, state registry, HIE, or some other protected resource.
Step 3: Configure the Authentication Protocol
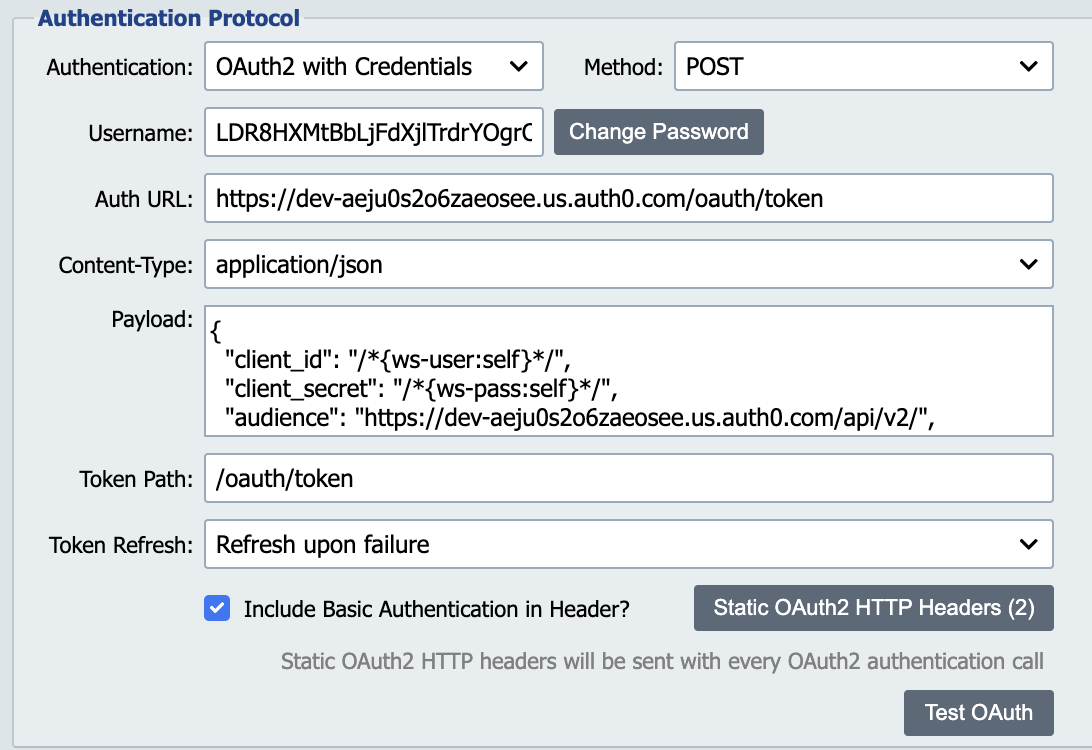
In the Authentication Protocol section, configure the following fields:
- Authentication:
OAuth2 with Credentials. - Method:
POST. - Username: the Auth0 Client ID from Step 1.
- Password: the Auth0 Client Secret from Step 1.
- Auth URL: the Auth0 token endpoint, for example:
- Content-Type:
application/json. - Payload: the JSON payload, with each
{ws-user:self}/{ws-pass:self}tag wrapped in a/* … */comment so the editor parses the payload as valid JSON: Replace the audience host with your own Auth0 domain. - Token Path:
/access_token. - Token Refresh:
Refresh upon failure.
Step 4: Test the connection
Click Save to persist the Web Service Connection.
Click Test OAuth. QIE posts the payload to the Auth URL and displays the response in the Test Log dialog. A successful response includes a JWT in the access_token field.
If the test fails, verify the Client ID, Client Secret, Auth URL, audience, and JSON syntax.
Step 5: Use the access token
As with the URL-encoded exercise, QIE stores the access token in a cookie associated with the Web Service Connection and automatically sends it as Authorization: Bearer <token> in the HTTP header on every subsequent call to the Resource Server made through a mapping node or destination node that references this connection.